
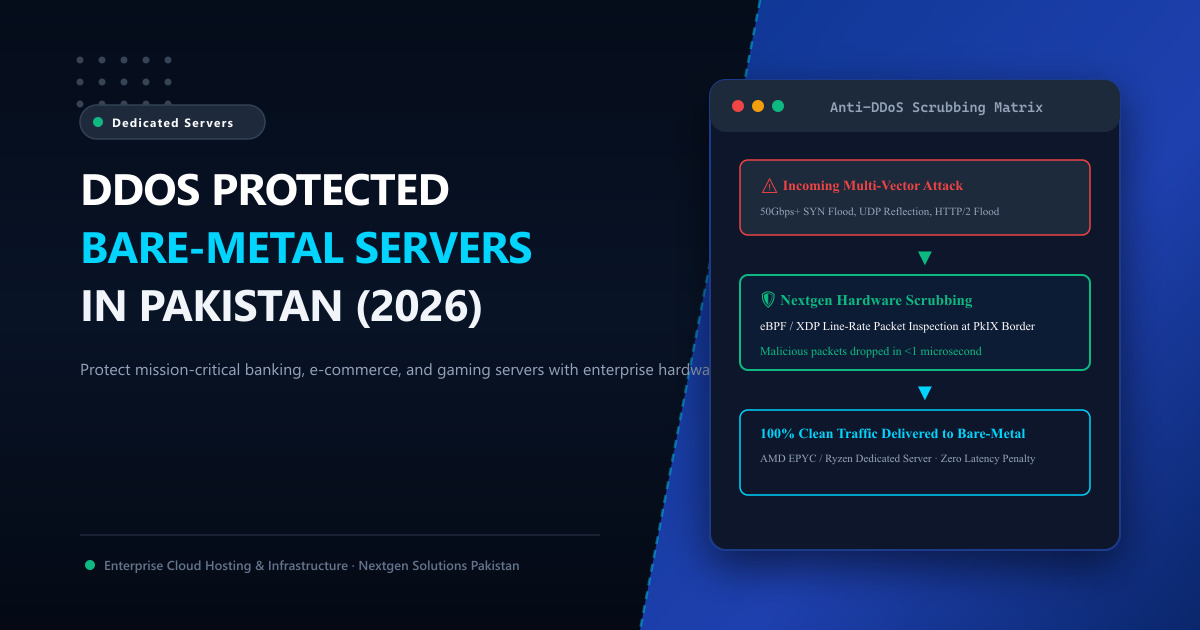
In 2026, the volume and sophistication of Distributed Denial of Service (DDoS) attacks targeting Pakistani digital infrastructure reached unprecedented heights.
From rival e-commerce competitors deploying cheap, rented booter/stressor botnets during seasonal flash sales, to state-sponsored volumetric floods targeting financial payment switches, and UDP reflection attacks targeting high-tick competitive gaming servers, an unprotected server can be completely crippled within seconds.
When an unmitigated 50 Gbps volumetric SYN or UDP flood hits an unhardened hosting IP:
- The upstream ISP uplink immediately saturates, triggering packet drops across the entire subnet.
- The server’s network interface card (NIC) and Linux kernel network stack choke on interrupt requests (IRQs), driving CPU load to 100%.
- Most budget hosting providers in Pakistan panic and null-route (blackhole) your IP address, taking your entire business offline for hours or days to protect their other customers.
To stay resilient against malicious adversaries, Pakistani enterprises and high-traffic platforms deploy DDoS-Protected Bare-Metal Dedicated Servers.
In this technical architectural guide, we dissect the mechanics of modern volumetric and Layer-7 DDoS attacks, explore multi-tier hardware scrubbing pipelines, and explain how Nextgen delivers line-rate mitigation with sub-15ms domestic latency.
🛡️ The Threat Landscape: Volumetric vs. Application-Layer Attacks
Modern cyberattacks rarely use a single protocol vector; they launch blended multi-vector offensives designed to overwhelm different layers of the OSI model:
[ OSI LAYER 3 / 4: Volumetric & Protocol Floods ]
Vectors: UDP Reflection (NTP, DNS, Memcached), TCP SYN Floods, ICMP Echo
Goal: Saturate physical transit bandwidth & exhaust Linux connection state tables
Defense: Upstream Hardware Scrubbing & BGP Anycast Divergence

[ OSI LAYER 7: Application & Resource Exhaustion ]
Vectors: HTTP/2 Rapid Reset, Slowloris, POST Floods, Recursive Search Queries
Goal: Exhaust PHP-FPM workers, Apache threads, and MySQL database connection pools
Defense: WAF (Web Application Firewall), eBPF/XDP rate-limiting, Behavioral AI| Attack Type | Target Component | Typical Attack Volume | Impact on Unprotected Server |
|---|---|---|---|
| UDP Amplification | Network Port & Bandwidth | 20 Gbps to 200+ Gbps | Instant pipe saturation; ISP null-routes IP. |
| TCP SYN Flood | Linux Kernel SYN Backlog | 10M to 50M Packets/Sec | Kernel drops legitimate TCP connection requests. |
| HTTP/2 Rapid Reset | Web Server (Nginx/Apache) | 100k to 1M Requests/Sec | Web server worker starvation; 502/504 errors. |
| Slowloris | Socket Connection Tables | <1 Mbps (Trickle of bytes) | Exhausts web server maximum concurrent connections. |
⚡ The Nextgen Hardware Mitigation Pipeline: How Scrubbing Works
When you deploy a DDoS-protected dedicated server with Nextgen, malicious traffic is filtered long before it ever reaches your physical machine:
[ Incoming Global & Domestic Traffic ]
                 │
                 ▼
[ Tier-1 Edge BGP Anycast Routing ]
   - Volumetric traffic is geo-dispersed across scrubbing centers
                 │
                 ▼
[ Hardware Scrubbing Appliances & eBPF/XDP Pipeline ]
   - Analyzes packet headers at line rate (100Gbps+ ASIC throughput)
   - Filters spoofed UDP reflection, invalid TCP flags, and SYN malformations
   - Drops malicious packets in <1 microsecond
                 │
                 ▼
[ Clean Traffic Delivered to Your Bare-Metal Server ]
   - Only verified, legitimate client requests reach your AMD/Intel CPU
   - Zero packet loss, zero CPU jitter, and sub-10ms domestic ping!
⚙️ Kernel-Level Optimization: Hardening Linux Network Stacks (SYSCTL)
While upstream hardware scrubbing handles multi-gigabit volumetric floods, hardening your bare-metal Linux kernel ensures your server can absorb protocol-level spikes without stuttering:
Edit /etc/sysctl.conf to optimize TCP backlog queues and drop malformed packets:
# Enable SYN Cookies (Protects against TCP SYN floods when backlog fills)
net.ipv4.tcp_syncookies = 1

# Increase max backlog of pending connections
net.ipv4.tcp_max_syn_backlog = 8192
net.core.somaxconn = 65535
net.core.netdev_max_backlog = 16384

# Reduce TCP FIN timeout to quickly free orphaned sockets
net.ipv4.tcp_fin_timeout = 15

# Disable ICMP Echo redirects and ignore broadcast pings
net.ipv4.icmp_echo_ignore_broadcasts = 1
net.ipv4.conf.all.accept_redirects = 0
net.ipv4.conf.default.accept_redirects = 0

# Protect against IP spoofing (Reverse Path Filtering)
net.ipv4.conf.all.rp_filter = 1
net.ipv4.conf.default.rp_filter = 1
Apply immediately without rebooting:
sudo sysctl -p🎮 Why Game Servers & Fintech Gateways Require Bare-Metal Protection
Unlike static brochure websites that can sit behind reverse proxies like basic Cloudflare CDN, stateful real-time applications cannot tolerate proxy buffering:
- Game Servers (Counter-Strike 2, Rust, FiveM, Minecraft): Players communicate over raw UDP sockets where latency, packet jitter, and tick rates are paramount. Cloudflare’s free or Pro tiers do not proxy arbitrary UDP ports, leaving game servers exposed.
- Fintech APIs & Banking Core Switches: Regulatory bodies like the State Bank of Pakistan (SBP) prohibit routing sensitive customer financial transactions through unvetted foreign proxy caches.
By provisioning high-core Dedicated Servers in Pakistan or global Dedicated Servers with native Layer-3/4 hardware scrubbing:
- All arbitrary TCP and UDP ports (including custom game ports and API sockets) are fully protected.
- Your players and banking clients enjoy direct, unthrottled 1Gbps to 10Gbps connectivity with zero proxy overhead.
- You maintain 100% data sovereignty on enterprise hardware in Tier-3 Islamabad datacenters.
📚 Related Technical Architecture Guides & Reading
- Colocation Hosting Benefits in Pakistan: Moving Beyond Office Closets – Physical security, N+1 redundant power, and Tier-3 datacenter defense.
- What is Dedicated Hosting: 100% Bare-Metal Performance Explained – Unshared hardware RAID arrays, unthrottled CPU cores, and IPMI control.
- Proxmox VE vs VMware ESXi: The Enterprise Hypervisor Playbook – Virtualization design and network bridge configurations.
Deploy DDoS-Protected Bare-Metal Dedicated Servers in Pakistan
Never get taken offline by botnets or competitors. Nextgen delivers enterprise AMD EPYC and Intel Xeon dedicated bare-metal servers equipped with hardware-level DDoS scrubbing, unthrottled 1Gbps uplinks, and sub-10ms PkIX peering in Islamabad.
